FedRAMP 20x Journey • In Progress
CrashPlan’s Path to FedRAMP 20x Certification
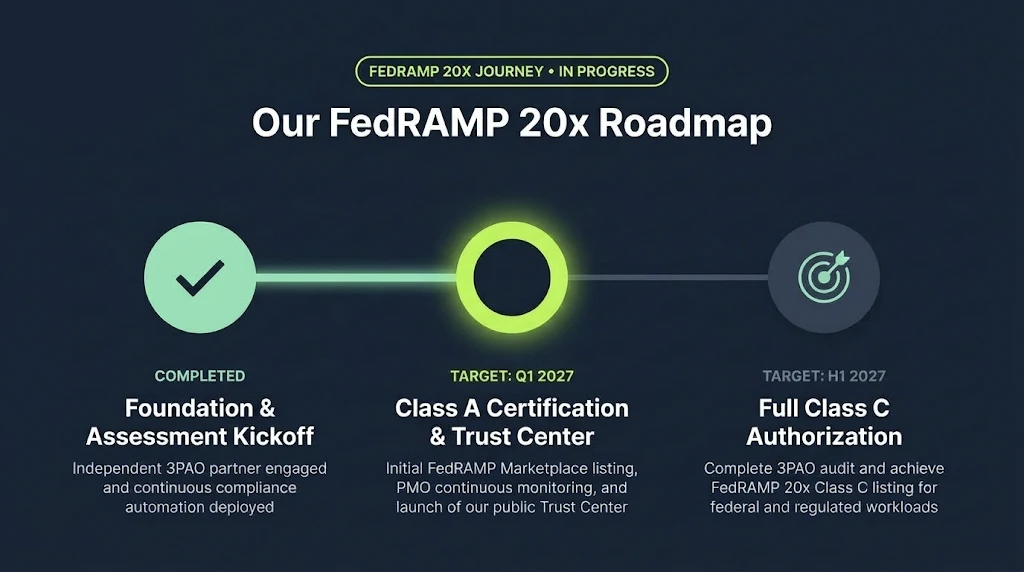
Targeting Class C certification in the first half of 2027. Reinforcing our commitment to meeting the security and compliance needs of government agencies and regulated organizations.
Built for Regulated & Public Sector Teams
Microsoft Azure Government
Hosted on Microsoft Azure Government infrastructure to meet federal cloud security standards.
Independent 3PAO Assessment
Audited by an accredited Third Party Assessment Organization to validate compliance.
Public Trust & Compliance Center
Self-service access to security certifications, audit reports, and compliance documentation.
Frequently Asked Questions
What is FedRAMP 20x and what does this mean for CrashPlan?
FedRAMP 20x is the modernized federal authorization framework designed to streamline cloud security assessments through automated, continuous validation rather than static point-in-time documentation. Achieving a FedRAMP 20x Class C listing on the FedRAMP Marketplace validates that CrashPlan meets rigorous federal security baselines for protecting sensitive data across government agencies, public sector entities, and regulated enterprises.
When do you expect to achieve Class C Certification?
We are targeting Class A certification in Q1 2027, followed by full FedRAMP 20x Class C listing on the FedRAMP Marketplace in H1 2027. Because FedRAMP authorization timelines depend on third-party audit schedules and PMO review, we will update our public roadmap as each milestone is completed.
How does this benefit current customers and commercial organizations?
Even if your organization does not require FedRAMP authorization, pursuing FedRAMP 20x strengthens CrashPlan’s overall security, governance, and continuous monitoring posture across the board. Regulated commercial teams—including those in healthcare, financial services, and defense contracting—directly benefit from the underlying cloud architecture enhancements, automated compliance controls, and expanded transparency.